# Existing Cluster with the AWS Observability accelerator base module and Infrastructure monitoring
---
This example demonstrates how to use the AWS Observability Accelerator Terraform
module with Infrastructure monitoring enabled.
The current example deploys the [AWS Distro for OpenTelemetry Operator](https://docs.aws.amazon.com/eks/latest/userguide/opentelemetry.html) for Amazon EKS with its requirements and make use of existing
Managed Service for Prometheus and Amazon Managed Grafana workspaces.
It is based on the `infrastructure monitoring`, one of our [workloads modules](../../modules/workloads/)
to provide an existing EKS cluster with an OpenTelemetry collector,
curated Grafana dashboards, Prometheus alerting and recording rules with multiple
configuration options on the cluster infrastructure.
## Prerequisites
Ensure that you have the following tools installed locally:
1. [aws cli](https://docs.aws.amazon.com/cli/latest/userguide/getting-started-install.html)
2. [kubectl](https://kubernetes.io/docs/tasks/tools/)
3. [terraform](https://learn.hashicorp.com/tutorials/terraform/install-cli)
## Setup
This example uses a local terraform state. If you need states to be saved remotely,
on Amazon S3 for example, visit the [terraform remote states](https://www.terraform.io/language/state/remote) documentation
1. Clone the repo using the command below
```
git clone https://github.com/aws-observability/terraform-aws-observability-accelerator.git
```
2. Initialize terraform
```console
cd examples/existing-cluster-with-base-and-infra
terraform init
```
3. AWS Region
Specify the AWS Region where the resources will be deployed. Edit the `terraform.tfvars` file and add `aws_region="..."`. You can also use environement variables `export TF_VAR_aws_region=xxx`.
4. EKS Cluster
To run this example, you need to provide your EKS cluster name.
If you don't have a cluster ready, visit [this example](https://github.com/aws-ia/terraform-aws-eks-blueprints/tree/main/examples/eks-cluster-with-new-vpc)
first to create a new one.
Add your cluster name for `eks_cluster_id="..."` to the `terraform.tfvars` or use an environment variable `export TF_VAR_eks_cluster_id=xxx`.
5. Amazon Managed Service for Prometheus workspace (optional)
If you have an existing workspace, add `managed_prometheus_workspace_id=ws-xxx`
or use an environment variable `export TF_VAR_managed_prometheus_workspace_id=ws-xxx`.
If you don't specify anything a new workspace will be created for you.
6. Amazon Managed Grafana workspace
If you have an existing workspace, add `managed_grafana_workspace_id=g-xxx`
or use an environment variable `export TF_VAR_managed_grafana_workspace_id=g-xxx`.
7. Grafana API Key
- Give admin access to the SSO user you set up when creating the Amazon Managed Grafana Workspace:
- In the AWS Console, navigate to Amazon Grafana. In the left navigation bar, click **All workspaces**, then click on the workspace name you are using for this example.
- Under **Authentication** within **AWS Single Sign-On (SSO)**, click **Configure users and user groups**
- Check the box next to the SSO user you created and click **Make admin**
- From the workspace in the AWS console, click on the `Grafana workspace URL` to open the workspace
- If you don't see the gear icon in the left navigation bar, log out and log back in.
- Click on the gear icon, then click on the **API keys** tab.
- Click **Add API key**, fill in the _Key name_ field and select _Admin_ as the Role.
- Copy your API key into `terraform.tfvars` under the `grafana_api_key` variable (`grafana_api_key="xxx"`) or set as an environment variable on your CLI (`export TF_VAR_grafana_api_key="xxx"`)
## Deploy
```sh
terraform apply -var-file=terraform.tfvars
```
or if you had setup environment variables, run
```sh
terraform apply
```
## Visualization
1. Prometheus datasource on Grafana
Open your Grafana workspace and under Configuration -> Data sources, you should see `aws-observability-accelerator`. Open and click `Save & test`. You should see a notification confirming that the AMP workspace is ready to be used on Grafana.
2. Grafana dashboards
Go to the Dashboards panel of your Grafana workspace. You should see a list of dashboards under the `Observability Accelerator Dashboards`
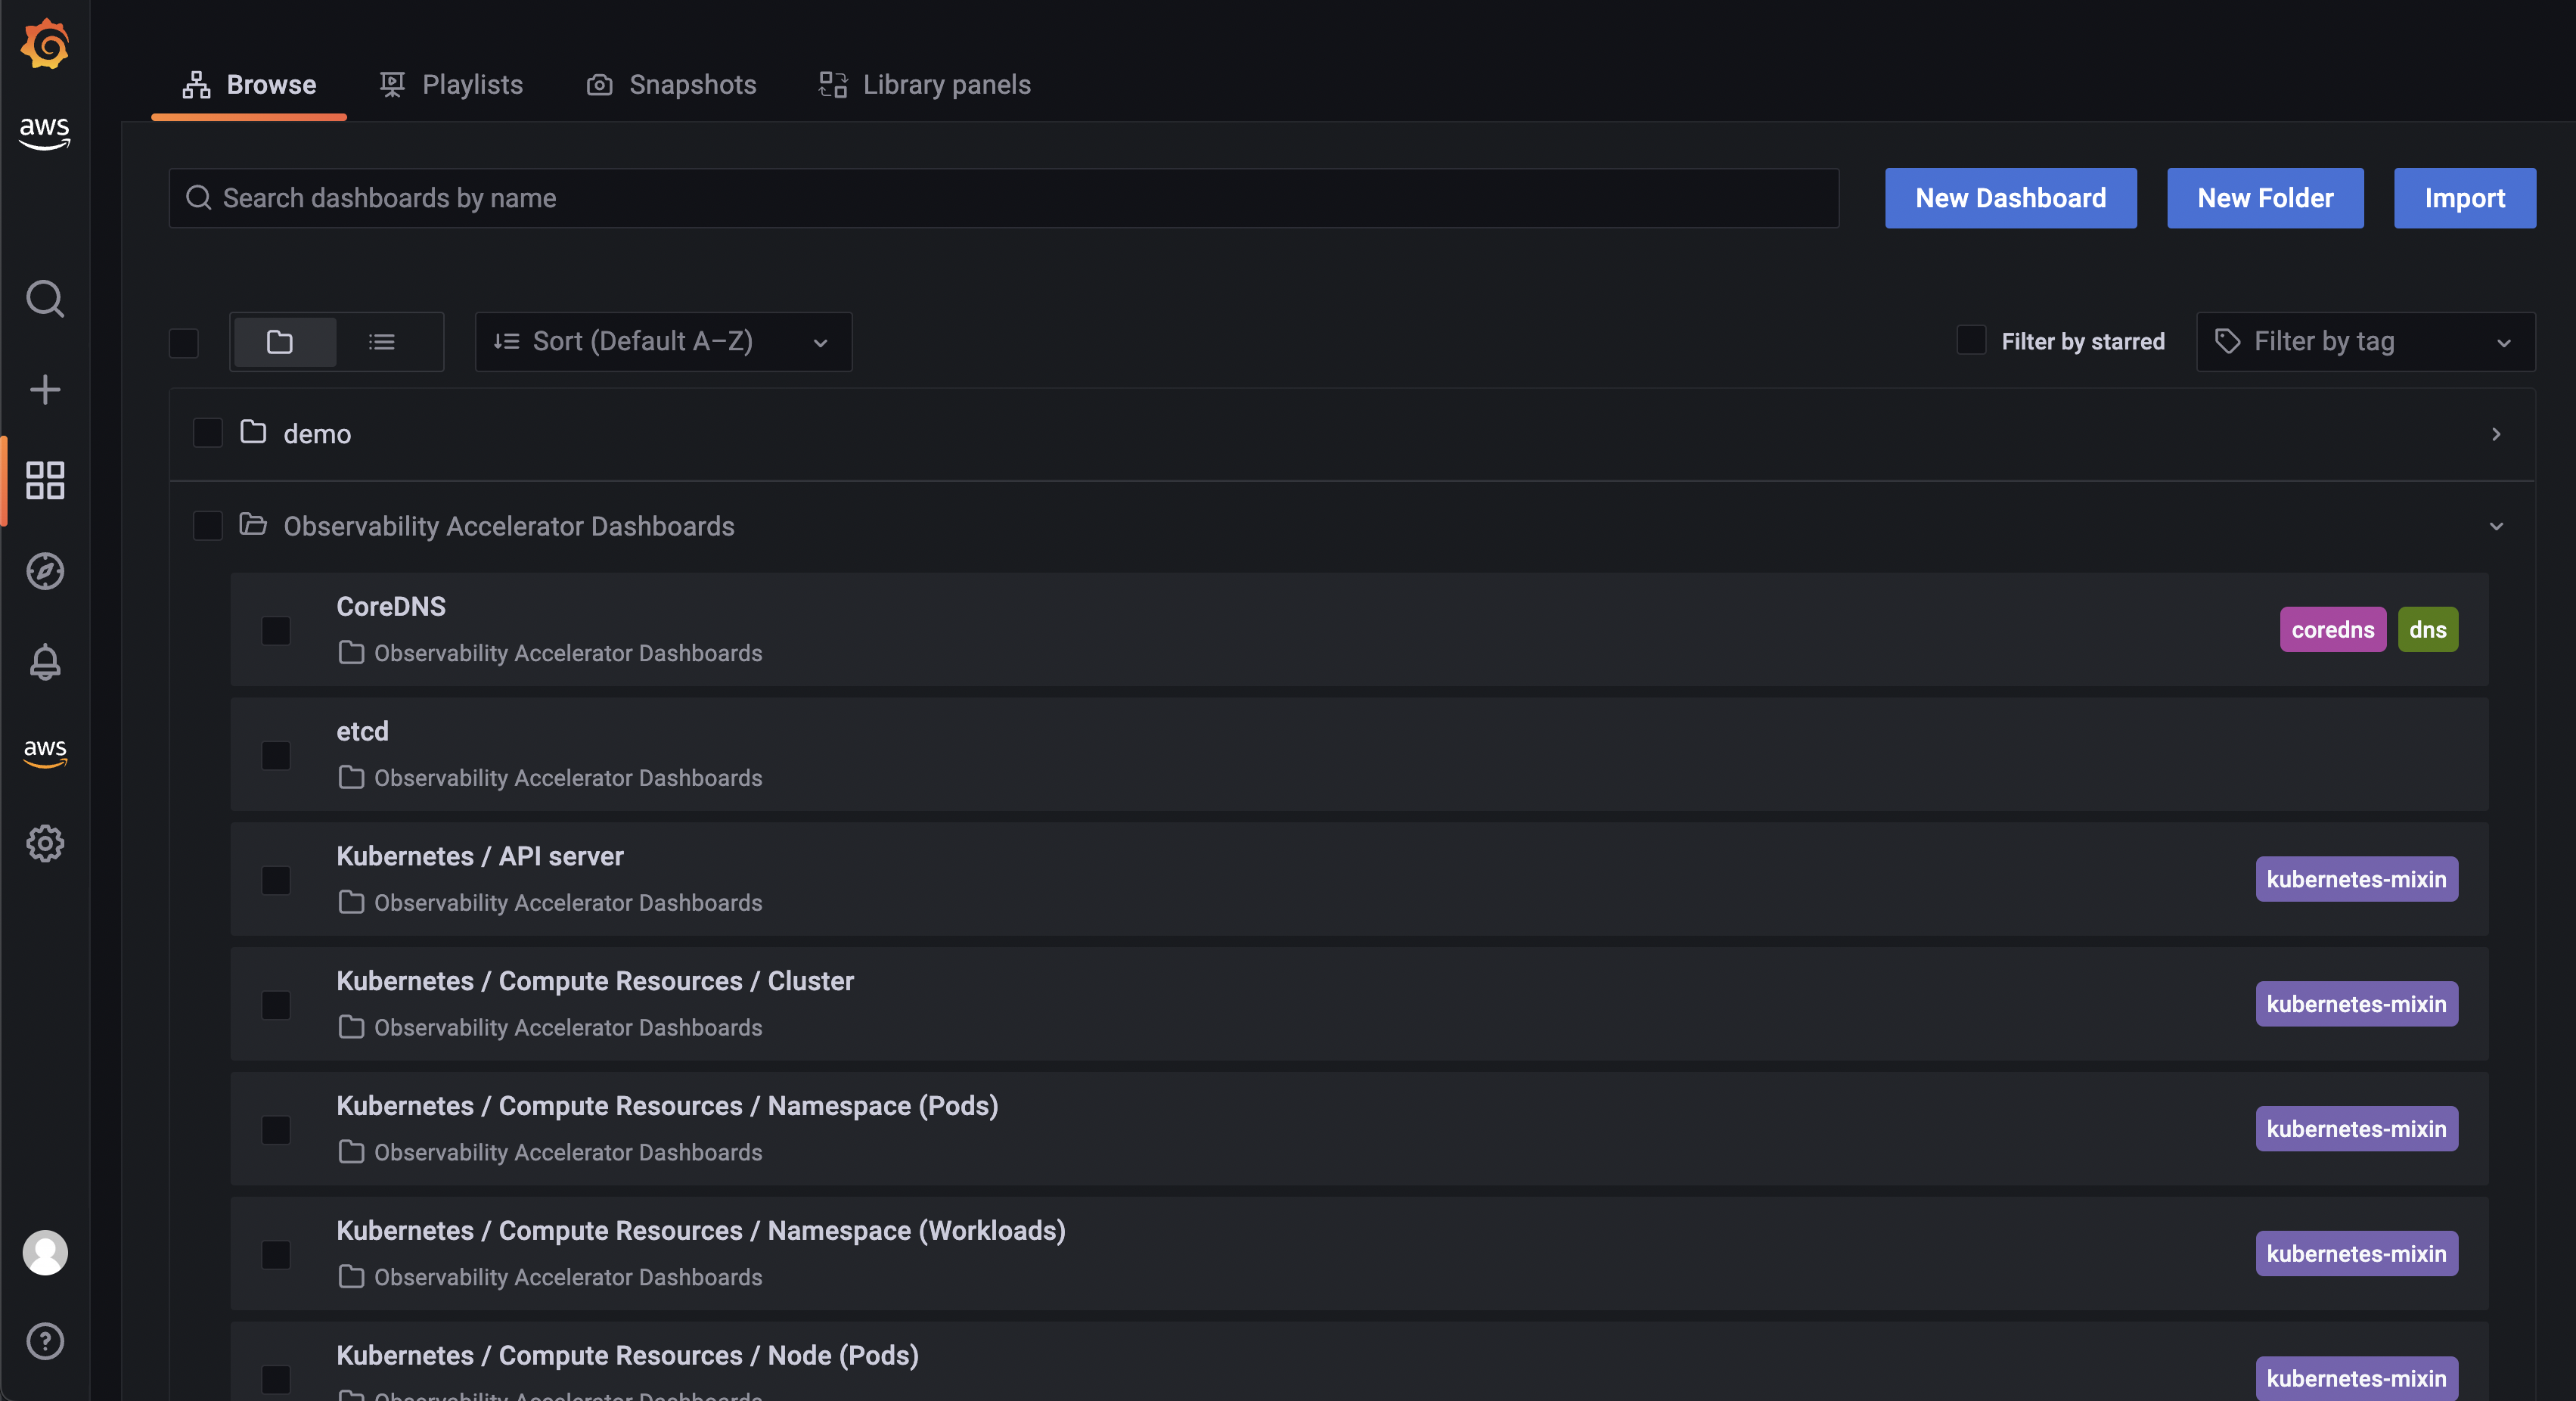 Open a specific dashboard and you should be able to view its visualization
 2. Amazon Managed Service for Prometheus (AMP) rules and alerts
Open the AMP console and view the details of your workspace. Under the `Rules management` tab, you should find new rules deployed.
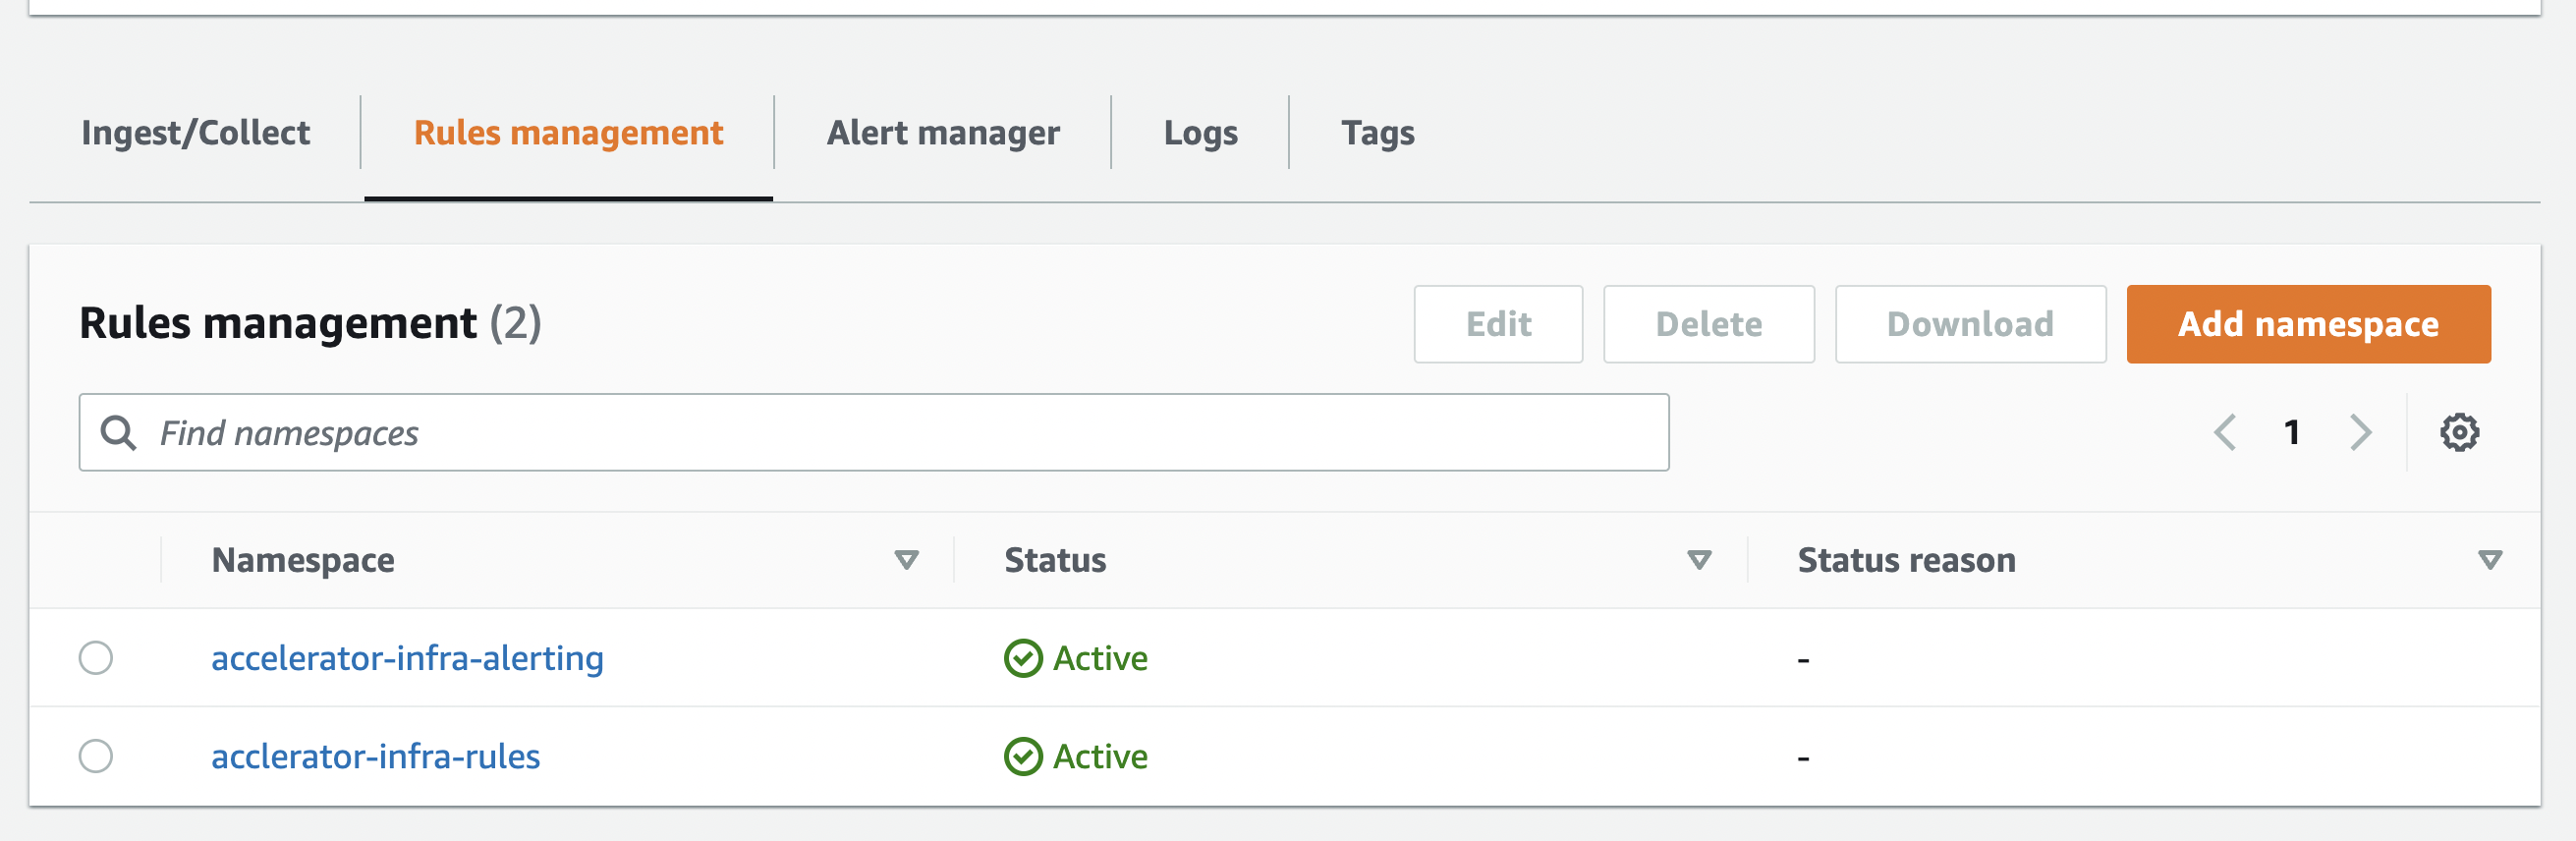 To setup your alert receiver, with Amazon SNS, follow [this documentation](https://docs.aws.amazon.com/prometheus/latest/userguide/AMP-alertmanager-receiver.html)
## Advanced configuration
1. Cross-region Managed Prometheus workspace
If your existing Managed Prometheus workspace is in another AWS Region,
add this `managed_prometheus_region=xxx` and `managed_prometheus_workspace_id=ws-xxx`.
2. Cross-region Managed Grafana workspace
If your existing Managed Prometheus workspace is in another AWS Region,
add this `managed_prometheus_region=xxx` and `managed_prometheus_workspace_id=ws-xxx`.
## Requirements
| Name | Version |
|------|---------|
| [grafana](#requirement\_grafana) | 1.25.0 |
## Providers
| Name | Version |
|------|---------|
| [aws](#provider\_aws) | n/a |
## Modules
| Name | Source | Version |
|------|--------|---------|
| [eks\_observability\_accelerator](#module\_eks\_observability\_accelerator) | ../../ | n/a |
| [workloads\_infra](#module\_workloads\_infra) | ../../modules/workloads/infra | n/a |
## Resources
| Name | Type |
|------|------|
| [aws_eks_cluster.this](https://registry.terraform.io/providers/hashicorp/aws/latest/docs/data-sources/eks_cluster) | data source |
| [aws_eks_cluster_auth.this](https://registry.terraform.io/providers/hashicorp/aws/latest/docs/data-sources/eks_cluster_auth) | data source |
## Inputs
| Name | Description | Type | Default | Required |
|------|-------------|------|---------|:--------:|
| [aws\_region](#input\_aws\_region) | AWS Region | `string` | n/a | yes |
| [eks\_cluster\_id](#input\_eks\_cluster\_id) | EKS Cluster Id | `string` | n/a | yes |
| [grafana\_api\_key](#input\_grafana\_api\_key) | API key for authorizing the Grafana provider to make changes to Amazon Managed Grafana | `string` | `""` | no |
| [grafana\_endpoint](#input\_grafana\_endpoint) | AMG endpoint | `string` | `null` | no |
| [managed\_grafana\_workspace\_id](#input\_managed\_grafana\_workspace\_id) | Amazon Managed Grafana (AMG) workspace ID | `string` | `""` | no |
| [managed\_prometheus\_endpoint](#input\_managed\_prometheus\_endpoint) | AMP workspace ID | `string` | `""` | no |
| [managed\_prometheus\_region](#input\_managed\_prometheus\_region) | Region where AMP is deployed | `string` | `""` | no |
| [managed\_prometheus\_workspace\_id](#input\_managed\_prometheus\_workspace\_id) | Amazon Managed Service for Prometheus (AMP) workspace ID | `string` | `""` | no |
## Outputs
| Name | Description |
|------|-------------|
| [aws\_region](#output\_aws\_region) | AWS Region |
| [eks\_cluster\_id](#output\_eks\_cluster\_id) | EKS Cluster Id |
| [eks\_cluster\_version](#output\_eks\_cluster\_version) | n/a |
| [prometheus\_endpoint](#output\_prometheus\_endpoint) | n/a |
| [prometheus\_id](#output\_prometheus\_id) | n/a |