 Rodrigue Koffi
8.3 KiB
Existing Cluster with the AWS Observability accelerator base module and Infrastructure monitoring
This example demonstrates how to use the AWS Observability Accelerator Terraform module with Infrastructure monitoring enabled. The current example deploys the AWS Distro for OpenTelemetry Operator for Amazon EKS with its requirements and make use of existing Amazon Managed Service for Prometheus and Amazon Managed Grafana workspaces.
It is based on the infrastructure monitoring, one of our workloads modules
to provide an existing EKS cluster with an OpenTelemetry collector,
curated Grafana dashboards, Prometheus alerting and recording rules with multiple
configuration options on the cluster infrastructure.
Prerequisites
Ensure that you have the following tools installed locally:
Setup
This example uses a local terraform state. If you need states to be saved remotely, on Amazon S3 for example, visit the terraform remote states documentation
- Clone the repo using the command below
git clone https://github.com/aws-observability/terraform-aws-observability-accelerator.git
- Initialize terraform
cd examples/existing-cluster-with-base-and-infra
terraform init
- AWS Region
Specify the AWS Region where the resources will be deployed. Edit the terraform.tfvars file and modify aws_region="...". You can also use environement variables export TF_VAR_aws_region=xxx.
- Amazon EKS Cluster
To run this example, you need to provide your EKS cluster name. If you don't have a cluster ready, visit this example first to create a new one.
Add your cluster name for eks_cluster_id="..." to the terraform.tfvars or use an environment variable export TF_VAR_eks_cluster_id=xxx.
- Amazon Managed Service for Prometheus workspace (optional)
If you have an existing workspace, add managed_prometheus_workspace_id=ws-xxx
or use an environment variable export TF_VAR_managed_prometheus_workspace_id=ws-xxx.
If you don't specify anything a new workspace will be created for you.
- Amazon Managed Grafana workspace
If you have an existing workspace, add managed_grafana_workspace_id=g-xxx
or use an environment variable export TF_VAR_managed_grafana_workspace_id=g-xxx.
- Grafana API Key
- Give admin access to the SSO user you set up when creating the Amazon Managed Grafana Workspace:
- In the AWS Console, navigate to Amazon Grafana. In the left navigation bar, click All workspaces, then click on the workspace name you are using for this example.
- Under Authentication within AWS Single Sign-On (SSO), click Configure users and user groups
- Check the box next to the SSO user you created and click Make admin
- From the workspace in the AWS console, click on the
Grafana workspace URLto open the workspace - If you don't see the gear icon in the left navigation bar, log out and log back in.
- Click on the gear icon, then click on the API keys tab.
- Click Add API key, fill in the Key name field and select Admin as the Role.
- Copy your API key into
terraform.tfvarsunder thegrafana_api_keyvariable (grafana_api_key="xxx") or set as an environment variable on your CLI (export TF_VAR_grafana_api_key="xxx")
Deploy
terraform apply -var-file=terraform.tfvars
or if you had setup environment variables, run
terraform apply
Visualization
- Prometheus datasource on Grafana
Open your Grafana workspace and under Configuration -> Data sources, you should see aws-observability-accelerator. Open and click Save & test. You should see a notification confirming that the Amazon Managed Service for Prometheus workspace is ready to be used on Grafana.
- Grafana dashboards
Go to the Dashboards panel of your Grafana workspace. You should see a list of dashboards under the Observability Accelerator Dashboards
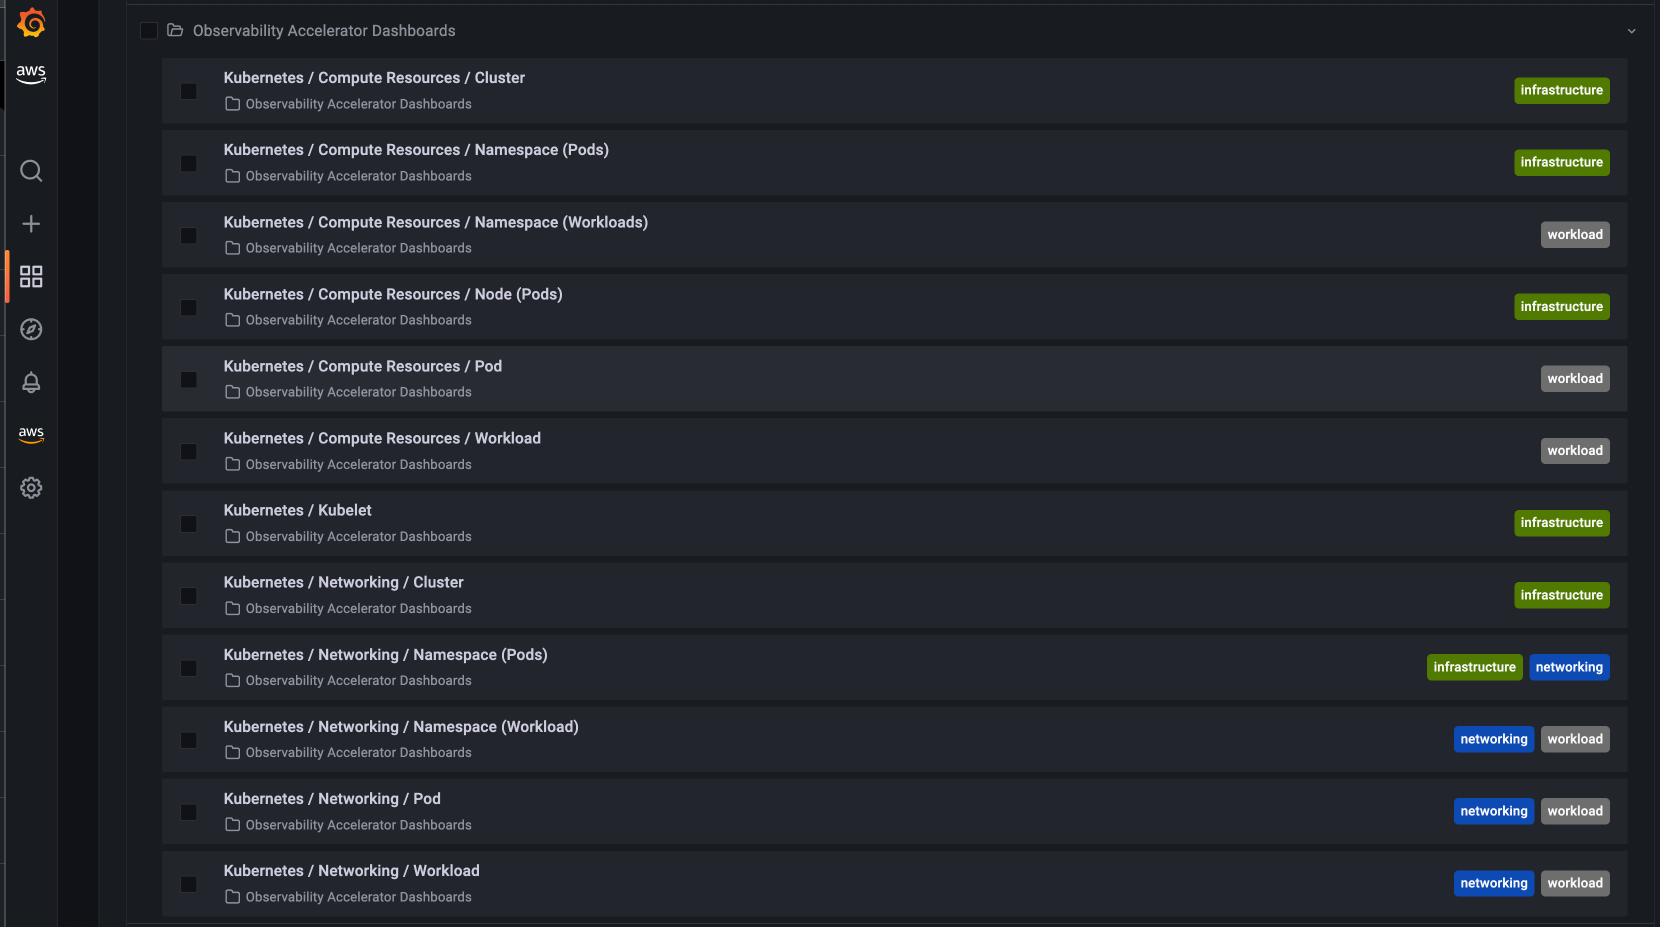
Open a specific dashboard and you should be able to view its visualization

- Amazon Managed Service for Prometheus rules and alerts
Open the Amazon Managed Service for Prometheus console and view the details of your workspace. Under the Rules management tab, you should find new rules deployed.
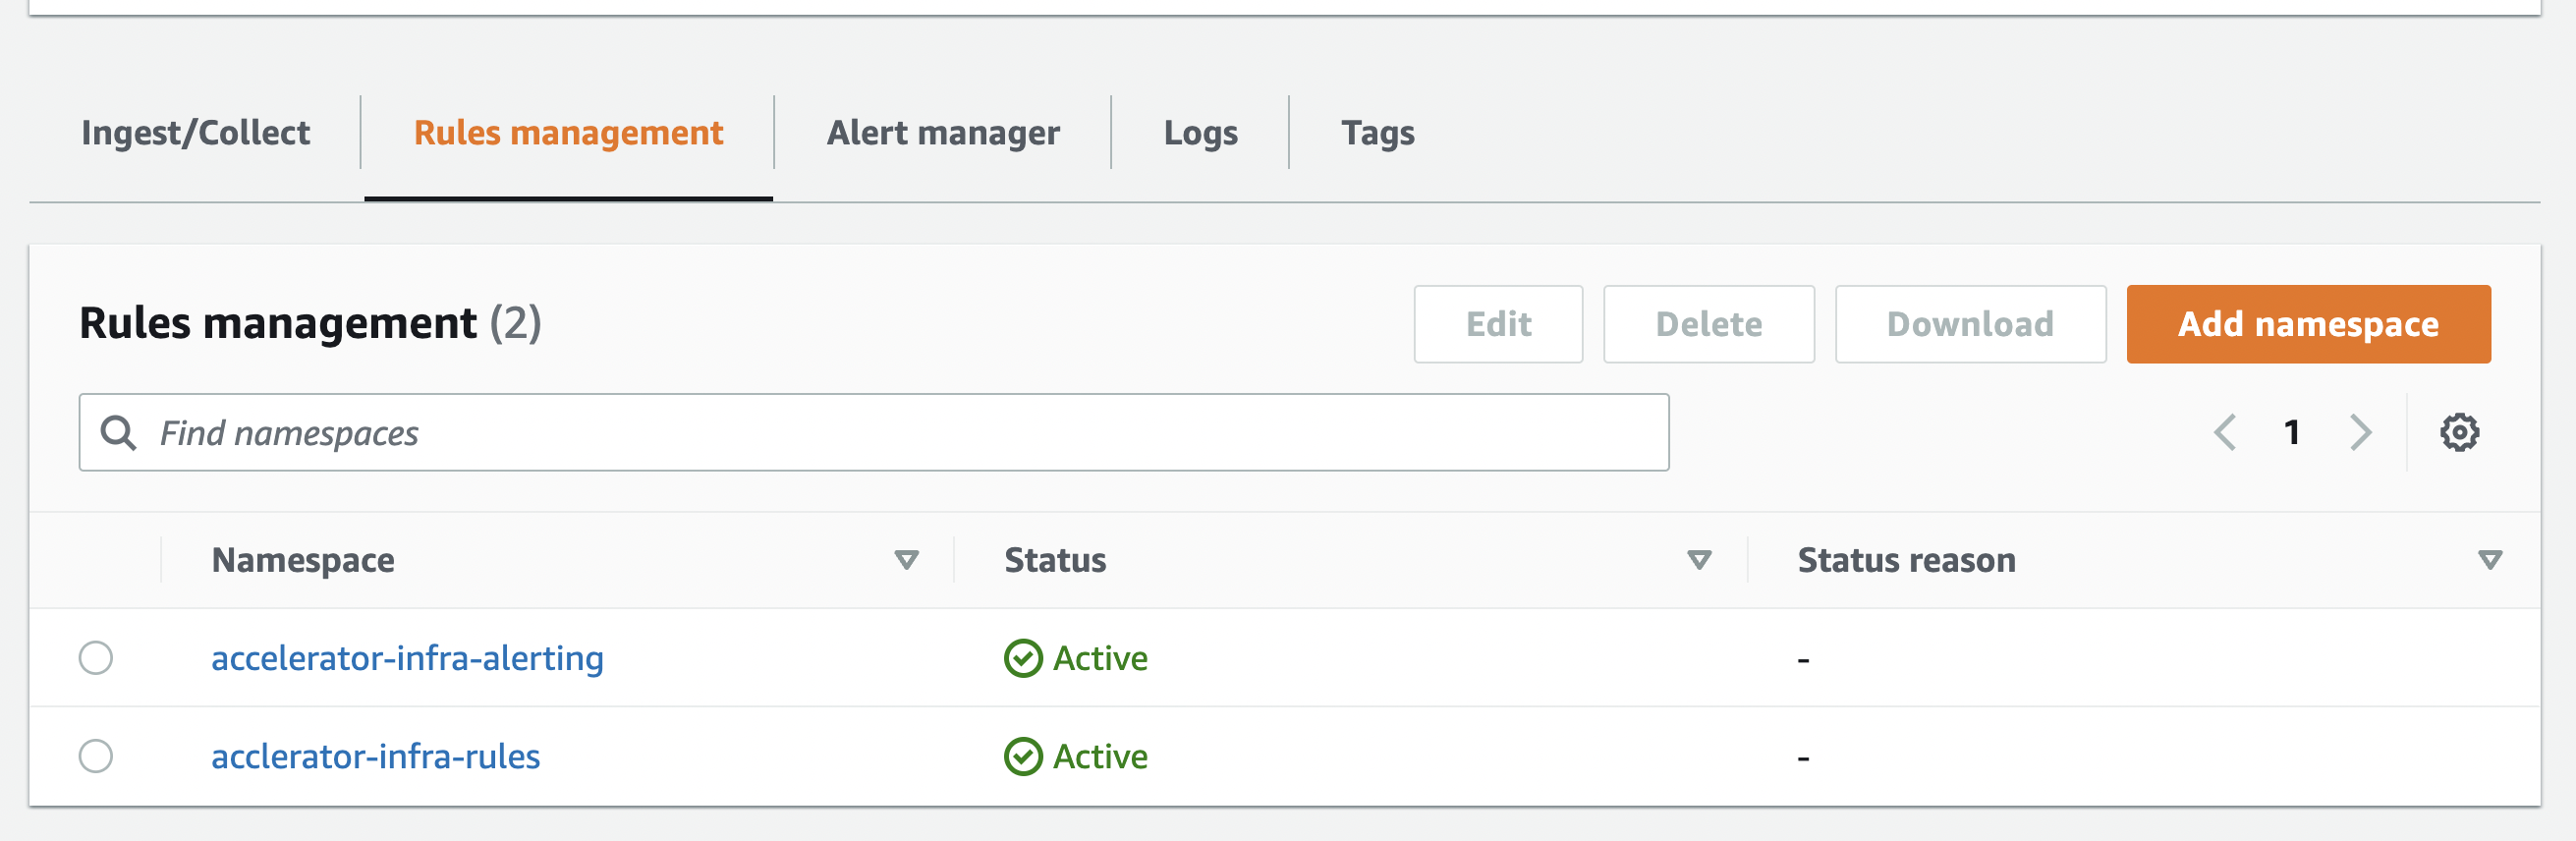
To setup your alert receiver, with Amazon SNS, follow this documentation
Advanced configuration
- Cross-region Amazon Managed Prometheus workspace
If your existing Amazon Managed Prometheus workspace is in another AWS Region,
add this managed_prometheus_region=xxx and managed_prometheus_workspace_id=ws-xxx.
- Cross-region Amazon Managed Grafana workspace
If your existing Amazon Managed Prometheus workspace is in another AWS Region,
add this managed_prometheus_region=xxx and managed_prometheus_workspace_id=ws-xxx.
Requirements
| Name | Version |
|---|---|
| grafana | >= 1.25.0 |
Providers
| Name | Version |
|---|---|
| aws | n/a |
Modules
| Name | Source | Version |
|---|---|---|
| eks_observability_accelerator | ../../ | n/a |
| workloads_infra | ../../modules/workloads/infra | n/a |
Resources
| Name | Type |
|---|---|
| aws_eks_cluster.this | data source |
| aws_eks_cluster_auth.this | data source |
Inputs
| Name | Description | Type | Default | Required |
|---|---|---|---|---|
| aws_region | AWS Region | string |
n/a | yes |
| eks_cluster_id | Name of the EKS cluster | string |
n/a | yes |
| grafana_api_key | API key for authorizing the Grafana provider to make changes to Amazon Managed Grafana | string |
"" |
no |
| managed_grafana_workspace_id | Amazon Managed Grafana Workspace ID | string |
"" |
no |
| managed_prometheus_workspace_id | Amazon Managed Service for Prometheus Workspace ID | string |
"" |
no |
Outputs
| Name | Description |
|---|---|
| aws_region | AWS Region |
| eks_cluster_id | EKS Cluster Id |
| eks_cluster_version | EKS Cluster version |
| managed_prometheus_workspace_endpoint | Amazon Managed Prometheus workspace endpoint |
| managed_prometheus_workspace_id | Amazon Managed Prometheus workspace ID |